
Cloud Security Incidents
Articles about cloud security breaches, credential theft, and incident response
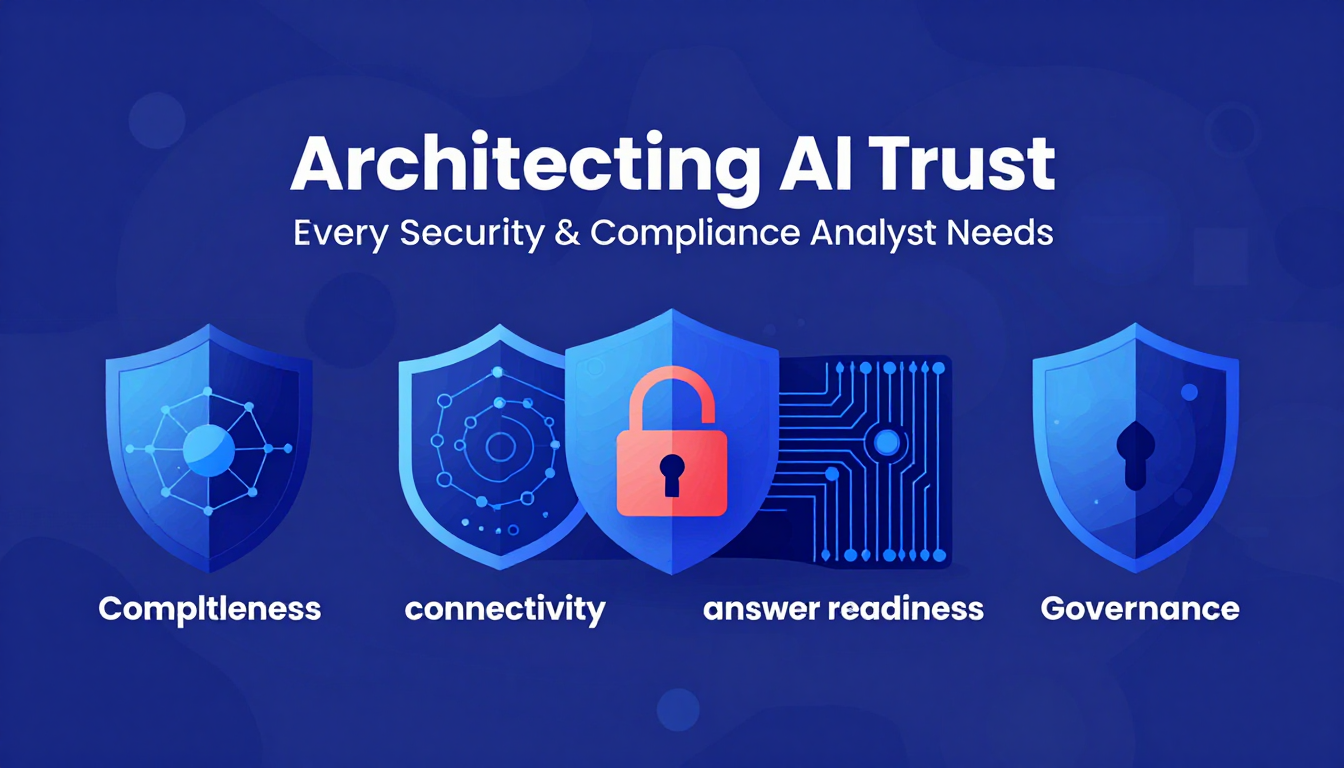
Architecting AI Trust: Four Knowledge Capabilities Every Security & Compliance Analyst Needs
A security & compliance analyst guide to building Brand Sovereignty through four core knowledge capabilities: completeness, connectivity, answer readiness, and governance.
How a Security & Compliance Analyst Reframes Regret into Post-Mortem Growth
Exploring the psychological nuances of regret through the lens of incident response. From ruminative self-flagellation to productive post-mortems, how security analysts turn missteps into systemic operational resilience.
Market Data Feeds and Delays: A Security & Compliance Analyst Guide to Real-Time vs Consolidated Feeds
Real-time stock quotes often reflect only single-exchange trades, while comprehensive multi-market quotes carry a mandatory 15-minute delay. Here is how a security & compliance analyst evaluates market data dissemination, feed architecture, and system auditability.
AI Temperature Sweeps: A Security & Compliance Analyst View on Medical Zebra Scans
How hyperparameter tuning and multi-sweep AI architectures prevent diagnostic blind spots in medical differential diagnosis and enterprise security compliance.
Bessent’s AI Sanctions Threat: A New Front in the IP Cold War
Treasury Secretary Scott Bessent signals potential U.S. sanctions on Chinese AI models. A security & compliance analyst examines IP theft, distillation, and risk in this new technological landscape.
Why the Security & Compliance Analyst Must Audit AI's Internal Workspace
Frontier AI interpretability is shifting from black-box evaluations to inner cognitive workspace monitoring. Here is how cognitive science and J-space interpretability impact the security & compliance analyst.
Uber's AV Ecosystem: A Security & Compliance Analyst Map of 30+ Deals
An in-depth analysis of Uber's 30+ autonomous vehicle partnerships and strategic investments through August 2026, evaluating third-party risk, data governance, and compliance challenges for platform orchestrators.
Why Every Security & Compliance Analyst Needs Deep Reading for Longevity
Emerging research shows reading printed books lowers 12-year mortality by 20% and preserves cognitive reserve. Here is what every security & compliance analyst must understand about mental stimulation.
Why the AI Hiring Rebound Signals a New Mandate for the Security & Compliance Analyst
Labor data and economic research show artificial intelligence augments enterprise productivity rather than driving mass layoffs, sparking a hiring rebound that demands expanded capabilities from every security & compliance analyst.
What Early-Life Sugar Rationing Teaches the Security & Compliance Analyst About Long-Term Risk
A landmark study analyzing post-WWII UK sugar rationing reveals that early-life sugar limits reduce long-term dementia risk by up to 23%. We examine the neuroimaging findings and what population-level risk analysis teaches modern analysts about system resilience.
UK Copilot Probe: Why Every Security & Compliance Analyst Must Audit M365 Renewal Defaults
The UK Competition and Markets Authority is investigating Microsoft over auto-renewing Copilot price hikes in Microsoft 365. Here is what a security & compliance analyst needs to audit.
What Aging Parents Want Every Security & Compliance Analyst to Understand About Autonomy and Governance
Balancing safety, agency, and communication with aging parents requires moving past rigid auditing habits toward structured, empathetic connection.