
Identity & Access
Authentication, credentials, IAM and zero-trust access control.
The AUR Rootkit Crisis: How 400+ Linux Packages Became a Credential-Theft Pipeline
Analysis of a supply chain attack targeting the Arch User Repository (AUR) where over 400 packages were compromised to distribute a Linux rootkit and credential-stealing infostealer malware, exploiting orphaned packages and modified PKGBUILD scripts to deliver eBPF-based rootkit capabilities and targeted credential theft from developer workstations.
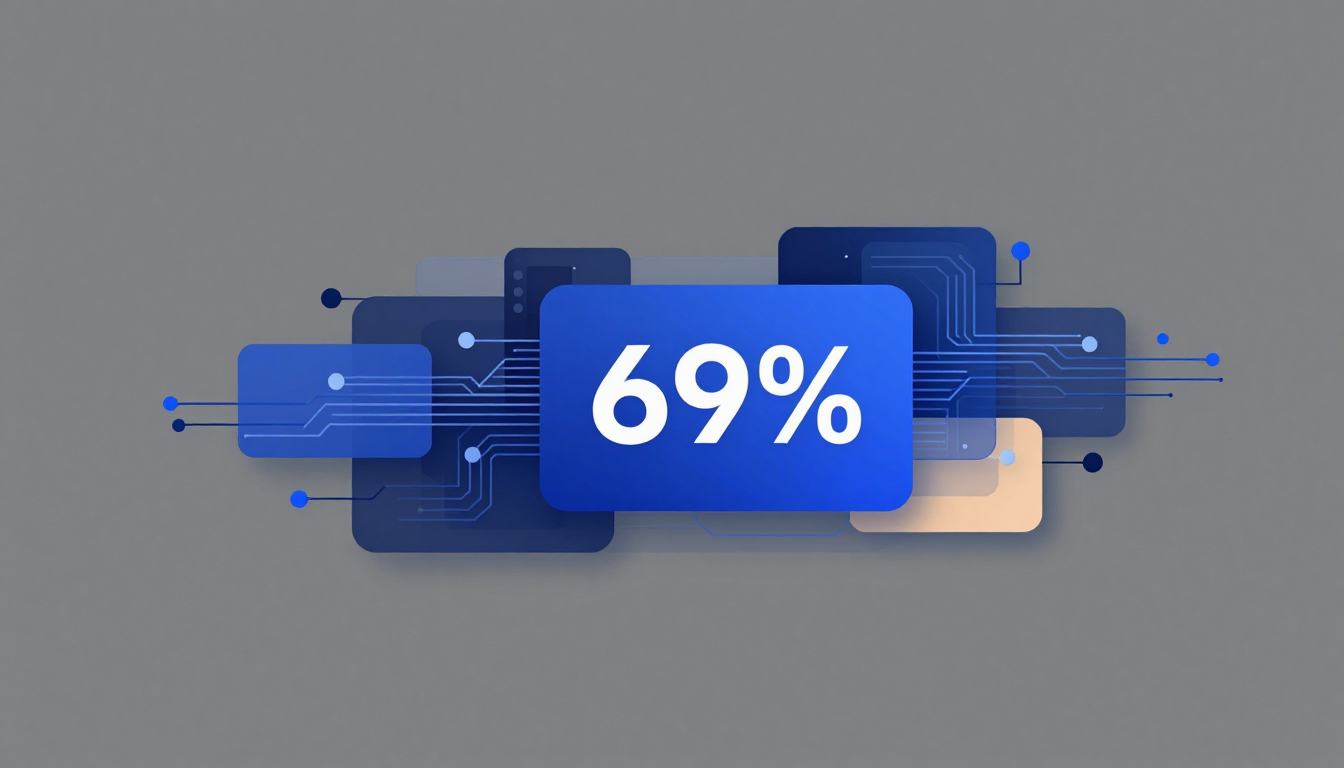
One Key to Rule Them All: The Danger of Shared Credentials in Enterprise AI Fleets
New survey data reveals that 69% of enterprises use shared credentials across their autonomous AI agent systems. This architectural shortcut creates a massive security flaw, enabling a single compromised agent to grant access to the entire fleet.
Apple's iOS 27 Will Fix Your Weak Passwords—If the Website Lets It
Apple's iOS 27 introduces an agentic password update feature, allowing users to automatically refresh compromised credentials with a single tap. But how well does it work in the real world?
Critical Authentication Bypass Vulnerabilities Affect BeyondTrust Remote Access Solutions
A professional analysis of critical authentication bypass security vulnerabilities in BeyondTrust Remote Support and Privileged Remote Access platforms, detail of the threat landscape, and mitigation steps.
Sobriety as Identity: How Quitting Alcohol Rewires Your Sense of Self
Exploring the psychological transformation of sobriety from a behavioral goal to a foundational identity, supported by neuroscience, environmental science, and coping strategy research.
The Evolution of Shai-Hulud: Anatomy of the Miasma Credential-Stealing Campaign
A detailed look at the Miasma attack framework, which leverages GitHub, credential-stealing, and AI-agent poisoning—following its brief intentional leak on GitHub—to propagate supply-chain attacks.
Industrial-Scale Credential Theft Campaign Linked to INC and Lynx Ransomware
A massive credential-harvesting operation, dubbed 'FortiBleed,' has been directly tied to the INC and Lynx ransomware-as-a-service groups, raising concerns about its role in fueling future network intrusions.
Beyond the UK: How Western Democracies are Confronting a Shared Institutional Crisis
The UK's current political turmoil is not an isolated event but a bellwether for structural instability facing many established Western democracies, fueled by a convergence of technological, economic, and institutional failures.
The Agentic AI Trap: When Autonomous Agents Outrun Identity Controls
Every technology wave forces security to play catch-up — but agentic AI moves at machine speed. As business units deploy autonomous agents with broad credentials, security leaders face an identity crisis traditional access controls were never built to solve.
When Login Isn't Enough: How Infostealers and Session Hijacking Are Breaking Identity Security
Organizations managing thousands of human and non-human identities across cloud, SaaS, endpoints, and remote environments face a new reality: credential abuse drives 22% of breaches, infostealer malware surged 84% in a single year, and session-token theft bypasses MFA entirely. This article examines the tactics attackers use to compromise accounts — from MFA fatigue and sophisticated phishing to endpoint-based credential harvesting — and why continuous verification is becoming essential.
Amazon Agrees to $2.25M Settlement After FTC Finds It Withheld Fraud Transaction Records from Identity Theft Victims
The U.S. Federal Trade Commission has reached a settlement with Amazon requiring the company to pay $2.25 million in civil penalties after finding that Amazon blocked identity theft victims from accessing records of fraudulent transactions made in their names, violating the Fair Credit Reporting Act.
Microsoft 365 Password Spraying Campaign Amplifies to 81 Million Login Attempts
An aggressive password-spraying campaign targeting Microsoft 365 environments generated over 81 million login attempts in two weeks by exploiting ROPC OAuth and flawed Conditional Access policies. Huntress tracked the attack from June 12–26, finding that 78 accounts across 64 orgs were compromised due to MFA gaps in Azure policies. This article breaks down how it happened, who was vulnerable, and what security teams need to lock down their conditional access today.