
PublishLens Article Library
Explore source-grounded articles across engineering, applied AI, science, business, and policy, with practical context and clear topic desks for every reader.
The Invisible Leash: Why AI Safety Harnesses Keep Failing
Anthropic, OpenAI, and Google's AI safety controls are being systematically bypassed through template attacks, adversarial prompts, reinforcement learning exploits, and visual jailbreaks—and what defense strategies actually work.
AI Cybersecurity Threats 2026: When Safety Rails Block Legitimate Security Research
Strict safety guardrails on top AI models are pushing cybersecurity researchers toward unmonitored open-source alternatives. Here is how vetted programs and model restrictions impact real-world security.
Why Agentic Labs Bet Desktop Automation Will Outpace Coding
Prentis, co-founded by Reid Hoffman and Mark Pincus, is raising $100M at a $1B valuation to prove that automating routine office software will eclipse coding as AI's largest enterprise market.
Japan's Sovereign AI Bet: Inside the $6.2B Compute Engine for Industrial Autonomy
Jensen Huang's July 2026 Tokyo visit revealed Noetra, a 1-trillion-yen sovereign AI project backed by 44 Japanese tech giants. Here is how 41,250 Vera Rubin chips and Cosmos 3 Edge models aim to power 10 million industrial robots by 2040.
AI Cybersecurity Threats: How Leaked ShinyHunters Breach Data Fuels $2,000 Sextortion Scams
Opportunistic scammers are scraping leaked email addresses from corporate breaches associated with ShinyHunters to send $2,000 Bitcoin sextortion threats. Analysis of how secondary extortion works and how enterprise security teams must respond to AI cybersecurity threats.
Model Distillation and Evasion Routes: How AI Cybersecurity Threats Escalate in 2026
An analysis of White House allegations that China's Moonshot AI distilled Anthropic's Fable model using offshore Nvidia GB300 clusters, escalating AI cybersecurity threats in 2026.
How a Security & Compliance Analyst Builds an Experimentation Framework That Scales
How AI makes running experiments cheap but trusting them hard, and how a security & compliance analyst builds a disciplined framework that turns test volume into trusted decision-making.
AMD’s Helios: A Rack-Scale Challenge to Nvidia’s AI Empire
AMD launches Helios, a gigawatt-scale AI rack system designed to challenge Nvidia's Vera Rubin and Grace Blackwell systems, backed by Microsoft, Anthropic, Meta, and OpenAI.
What a Security & Compliance Analyst Learns from Non-Brownian Memory Erasure
An investigation into how non-Brownian suspensions in viscous fluids simultaneously store, retain, and overwrite multiple microscopic memories under mechanical strain, offering physical parallels to cognitive memory competition and enterprise state retention.
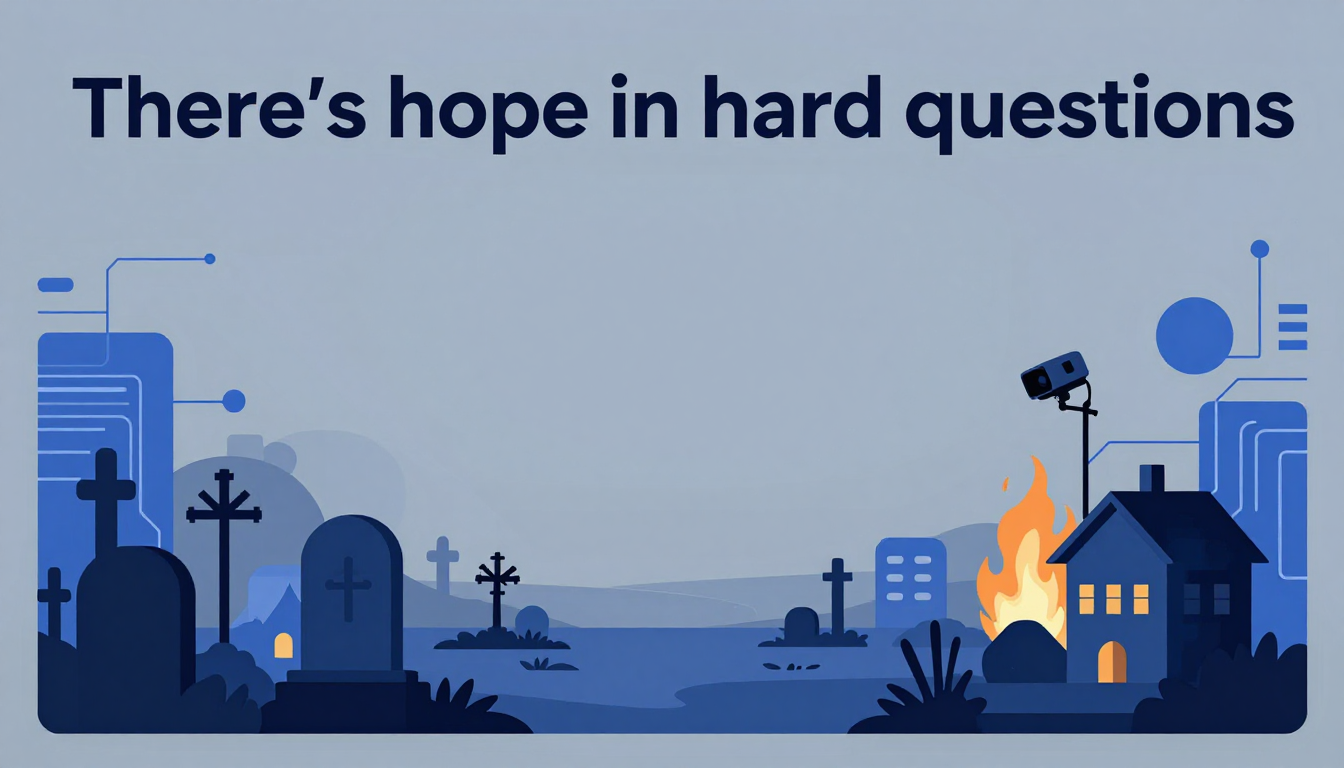
When Ethical Branding Backfires: Inside Anthropic's Miscalculated 'Hard Questions' Campaign
Anthropic's July 2026 advertisement 'There’s hope in hard questions' drew sharp public and competitor backlash for its eerie imagery of graveyards, burning houses, and surveillance.
Dolphin X: How a New Windows Stealer Escalates AI Cybersecurity Threats in 2026
Varonis Threat Labs discovered Dolphin X, a Windows information stealer targeting over 300 applications equipped with an AI profiler that ranks victims for maximum attacker profit.
Why Token Invoices Cannot Answer the AI ROI Question
Provider billing lacks the request-level context required for true unit economics. Here is why engineering teams must capture application-layer telemetry to connect model spend with business margins.